OpenAI Employee Arrest Raises AI Security Questions
You trust AI companies with code, customer data, research notes, and business plans. That trust gets tested when security problems move from abstract risk to a police report. The recent OpenAI employee arrest, reported by The Verge, puts a harsh spotlight on how AI labs manage physical security, internal trust, and employee conduct at a time when every meeting can carry strategic value. Details remain limited, and that matters. Still, the incident is useful because it exposes a larger issue that has been building for years. AI firms are now closer to defense contractors, cloud giants, and chip companies than old-school software startups. Their offices hold valuable intellectual property, sensitive partnerships, and competitive roadmaps. If security teams treat them like ordinary tech workplaces, they are playing the wrong sport.
What Matters Most
- The OpenAI employee arrest is a security signal, not just a workplace oddity.
- AI companies need stronger controls around meetings, devices, visitor access, and internal investigations.
- Physical security now matters as much as cybersecurity for major AI labs.
- Employees deserve clear rules, fair process, and privacy boundaries.
- Customers should ask AI vendors how they protect confidential information inside the company.
What The Verge Reported About the OpenAI Employee Arrest
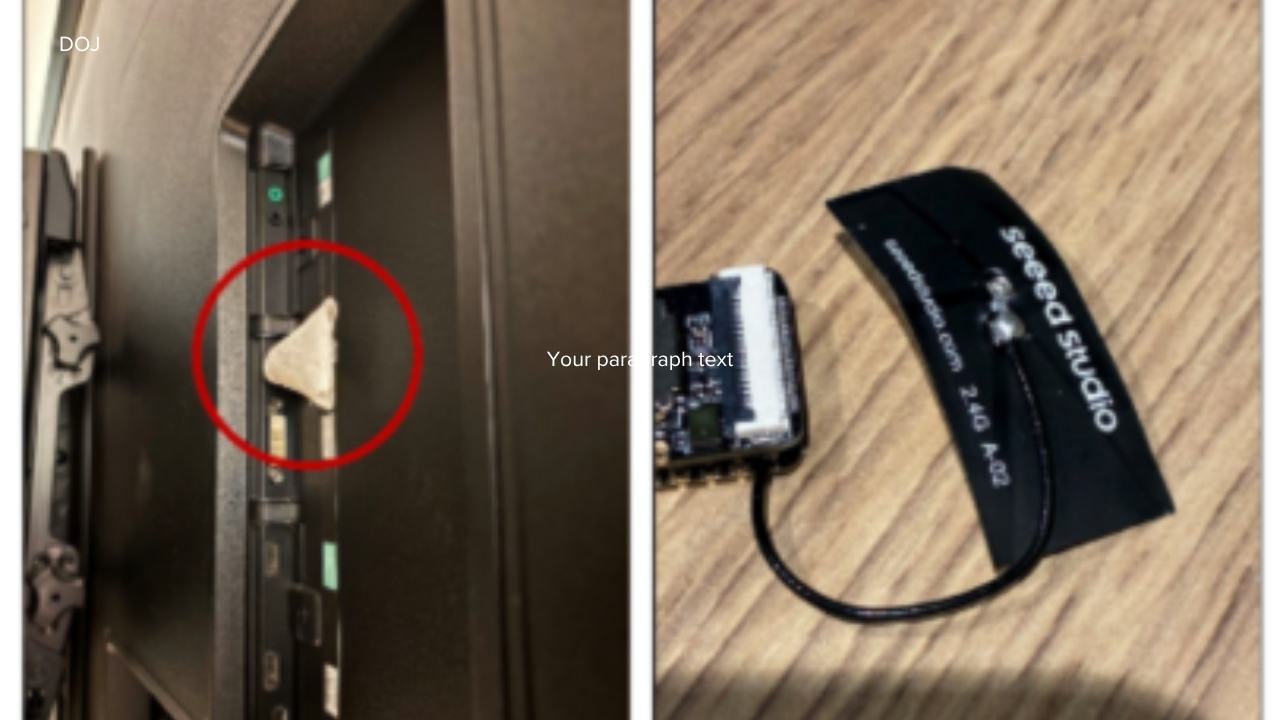
The Verge reported that an OpenAI employee was arrested after a recording device was allegedly found. The report centers on the presence of that device and the legal action that followed. Public information is still narrow, so the smartest reading is cautious.
That does not make the story small.
Recording devices inside a major AI company raise immediate questions. Was the device used? What was it meant to capture? Did it involve trade secrets, private conversations, employee disputes, or something else entirely? We should avoid filling gaps with guesses, but security leaders should not ignore the pattern.
My read: the most useful lesson is not about one person. It is about whether AI companies have grown their internal safeguards as fast as their market power.
Why the OpenAI Employee Arrest Matters for AI Security
AI labs are magnets for sensitive information. They handle model weights, safety evaluations, product launch plans, customer contracts, government relationships, and data handling practices. A stray recording from the wrong room could expose more than office gossip.
Think of an AI company like a professional sports locker room during playoffs. Strategy, injury updates, and internal tension all have value before the public sees the result. One hidden microphone changes the room. People speak differently, trust drops, and the competitive stakes shift.
For years, the industry focused on network security. Firewalls, access tokens, bug bounties, and SOC 2 reports became the visible proof points. But the physical layer is back. Laptops, badges, conference rooms, phones, smart glasses, USB devices, and portable recorders are now part of the threat model.
What AI Companies Should Do After the OpenAI Employee Arrest
Look, security theater will not help. Bag checks and scary posters are easy. Real protection needs policy, tooling, and judgment.
- Classify meetings by sensitivity. A routine product sync does not need the same controls as a model safety review or partnership negotiation.
- Create device rules people can understand. Ban vague language. Say which devices are allowed, where they are allowed, and who can approve exceptions.
- Use secure rooms for high-risk discussions. That can include device lockers, controlled entry, and periodic sweeps by trained staff.
- Limit access by need, not status. Seniority should not automatically grant entry to every sensitive conversation.
- Document investigation procedures. Employees need to know how allegations are handled, who reviews evidence, and what rights they have.
And here is the uncomfortable bit. AI companies often move too fast for their own governance teams. Product groups sprint ahead, security teams try to catch up, and legal teams get pulled in after the damage. That rhythm worked poorly in social media. It will work worse in AI.
Employee Privacy Is Part of AI Security
There is another side to this. Companies cannot respond to one alleged recording device by turning every office into a surveillance box. That would be a bad trade.
Employees at AI labs already work under intense pressure. They deal with confidential projects, media attention, internal politics, and the ethical weight of systems used by millions. If management answers every incident with blanket monitoring, the workplace gets colder and less honest. Who wants to raise a safety concern in a room that feels wired from every angle?
Good security draws clean lines. It protects sensitive work without treating every employee as a suspect. That means narrow monitoring, written policies, independent review, and escalation paths outside a direct manager when needed.
What Customers Should Ask AI Vendors Now
If your company buys AI tools or shares proprietary data with a vendor, this story should push you to ask better questions. Not alarmist questions. Specific ones.
- How do you restrict access to customer data and internal model details?
- Do you classify sensitive meetings and rooms?
- What is your policy on recording devices, phones, wearables, and transcription tools?
- How do you investigate suspected insider risk?
- Who can access audit logs, and how long are they retained?
- Do contractors follow the same physical security rules as employees?
Procurement teams love security questionnaires, but many still tilt toward cloud controls and compliance badges. Ask about the office, too. The human layer is where neat checklists start to wobble.
The OpenAI Employee Arrest and the Insider Risk Problem
Insider risk is hard because it mixes technology, behavior, and trust. The person with access may be an employee, contractor, visitor, vendor, or executive. The motive may be money, activism, curiosity, coercion, or a personal dispute.
The OpenAI employee arrest is not proof of a broader insider threat crisis. But it lands during a period when AI companies face pressure from rivals, regulators, investors, and governments. The more valuable the research, the more tempting the access.
This is where AI firms need to borrow from financial institutions and national labs. Separate duties. Log access. Train people on reporting channels. Keep sensitive meetings small. Practice incident response before something happens. Boring work, yes. Non-negotiable work, too.
What Happens Next
The legal process should run on facts, not online speculation. The public may learn more through court records, company statements, or follow-up reporting. Until then, the industry should treat the story as a prompt to inspect its own weak spots.
The next AI security breach may not start with a hacked server. It may start in a conference room, with a device nobody noticed, during a meeting everyone assumed was private. If you run security, legal, procurement, or operations, ask the awkward room-level questions now.