OpenAI Safety Researchers Cut Raises Trust Questions
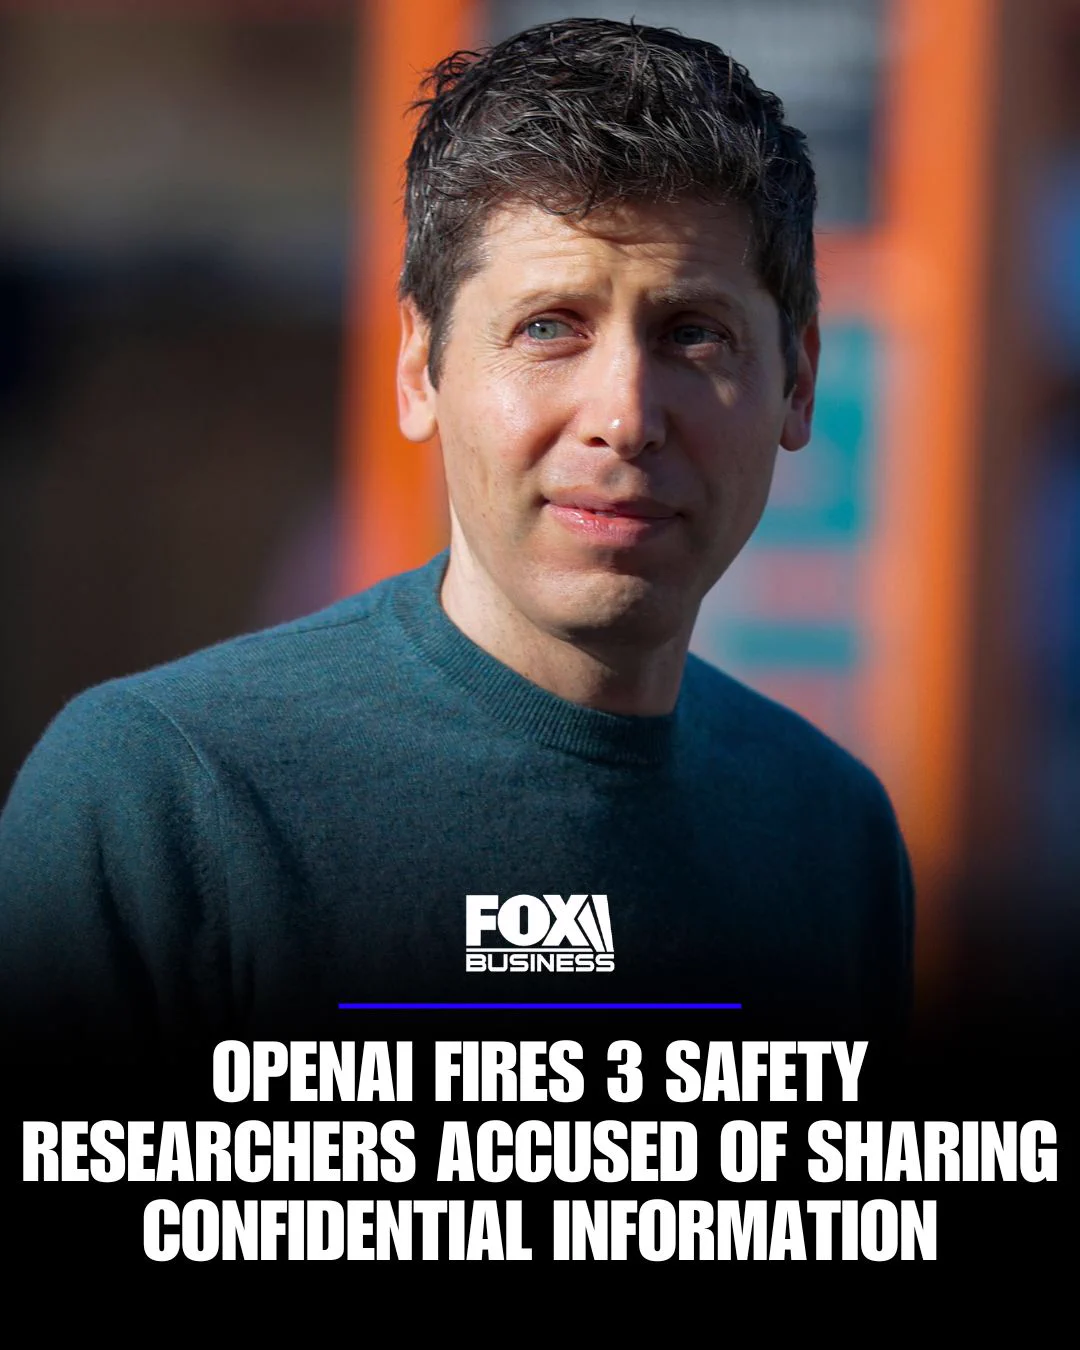
If you build on OpenAI, regulate AI, or simply use ChatGPT at work, the latest report about OpenAI safety researchers deserves your attention. TechCrunch, citing The Wall Street Journal, reported that OpenAI cut ties with three safety researchers, a move that lands at a sensitive time for the company and the wider AI industry. Safety teams are not public relations ornaments. They test systems, challenge release timelines, and ask awkward questions before products reach millions of users. That work matters more as frontier models move into coding, search, education, customer service, and workplace automation.
The issue is not whether one company can change its research roster. Of course it can. The harder question is whether the people tasked with stress-testing powerful AI systems can disagree without becoming expendable. That is the part enterprise buyers, policymakers, and developers should watch closely.
What Stands Out
- TechCrunch reported the cuts based on a Wall Street Journal story about three OpenAI safety researchers.
- The report adds pressure to OpenAI at a time when AI safety, governance, and model release speed are under close review.
- Research independence matters because internal safety work often spots risks before customers or regulators do.
- Companies using frontier AI should ask vendors how safety concerns are escalated, documented, and resolved.
Why OpenAI Safety Researchers Matter More Than Ever
OpenAI sits near the center of the AI market, which means its internal choices ripple outward. If a leading lab changes how it handles safety dissent, smaller labs may read that as a signal about what gets rewarded and what gets sidelined.
Good safety researchers are paid to be inconvenient. They probe models for misuse, deception, data leakage, bias, cybersecurity risks, and weak guardrails, often while product teams want to ship faster and investors want growth.
Safety research only has teeth if researchers can raise hard concerns before a launch, not after a press cycle goes wrong.
That tension is now public.
Look, no outsider can judge the full employment context from a headline. But the optics are rough because OpenAI has already faced questions about governance, board oversight, executive control, and the balance between safety and commercial pressure.
OpenAI Safety Researchers and the Problem of Internal Dissent
The best AI labs need internal critics the way a bridge project needs structural engineers. You do not invite them in because they make the ribbon-cutting prettier, you invite them because gravity does not care about your launch calendar.
What happens when those critics lose influence? Risk does not vanish. It moves into user reports, regulatory filings, press leaks, lawsuits, and customer churn.
What buyers should ask now
If your company depends on OpenAI models or any frontier AI provider, treat this as a procurement issue, not gossip from Silicon Valley. Ask direct questions and expect specific answers.
- Who can stop or delay a model release? A safety team without escalation power is a review committee with nicer stationery.
- How are safety objections recorded? Written records matter because memory gets fuzzy after a product launch.
- Can researchers publish negative findings? Total secrecy may protect intellectual property, but it can also bury risk signals.
- What changed after past incidents? Vendors should point to process changes, model changes, or policy updates.
- How does the company handle dissent? A mature lab should tolerate documented disagreement, even when it slows the roadmap.
These questions are not anti-AI. They are basic vendor management, especially if you plan to put AI into finance, health, legal, hiring, education, or security workflows.
The Governance Signal Behind the OpenAI Safety Researchers Report
OpenAI has long tried to straddle two identities. It presents itself as a company chasing advanced AI products, while also claiming a mission tied to safe and broadly beneficial artificial intelligence.
That dual role creates friction. A lab can say safety is non-negotiable, but the market watches what happens when safety work conflicts with product velocity, revenue targets, or partnership demands.
Regulators will watch too. The European Union AI Act, White House AI commitments, and emerging national safety institutes all push companies toward stronger testing, documentation, and accountability, even if the details vary by region.
Why this may affect regulation
Reports like this give policymakers a simple talking point. If top AI labs cannot show stable, independent safety functions, governments will feel more pressure to set outside rules.
That does not mean every personnel move should trigger a new law. But repeated signals of internal strain can harden the case for audits, incident reporting, whistleblower protections, and third-party evaluations.
What Developers Should Do If They Use OpenAI
Developers do not need to panic or rip out APIs overnight. They do need to reduce blind dependence, especially for features where model failures can create legal, financial, or safety exposure.
- Log model behavior in high-risk workflows. You need evidence if outputs drift or a vendor changes a model.
- Use fallback paths. A second provider, a smaller open model, or a human review queue can keep you from being boxed in.
- Write your own risk tests. Do not rely only on vendor safety claims, because your use case may be weird in ways their test suite missed.
- Review release notes and policy updates. Quiet model changes can affect performance, refusals, latency, and compliance.
- Separate demo quality from production trust. A model that impresses in a sales call may still fail under messy real traffic.
Here is the thing. AI vendors sell capability, but customers inherit part of the risk, and that risk grows when the vendor’s internal safety culture looks unstable.
The Bigger Bet: Speed or Trust?
OpenAI is not the only company facing this pressure. Anthropic, Google DeepMind, Meta, xAI, and other major labs all face the same collision between faster model releases and slower safety work.
The market often rewards speed first. Users notice new features before they notice better red-teaming, and investors rarely cheer a delayed launch caused by a safety review.
But trust compounds. If customers believe a lab suppresses inconvenient safety concerns, they will demand tighter contracts, more audits, and more ways to switch providers.
What should a serious AI company do after a report like this? It should explain how safety concerns are handled, who has authority to pause deployment, and how independent researchers can challenge product decisions without risking their careers.
What To Watch Next
The next signal will not be a slogan about responsible AI. It will be whether OpenAI and its peers give safety teams real power, real protection, and enough daylight for outsiders to judge the process.
If you depend on these models, ask your vendor one plain question this week: who inside the company is allowed to say no?